TL;DR: Most PDF signing insecurity does not show up as a hack. It shows up as a disputed signature nobody can defend, a document opened by the wrong person, or a compliance review that finds no real evidence behind a vendor's security page. You resolve this before you buy, not after, by testing claims instead of reading them. Run a real document through a trial account, pull the audit record, and check that it names who signed, how they were verified, and whether the file can prove it was not altered.
Nobody chooses a PDF signing tool because they want weak security. They choose it because the demo looked clean, the pricing worked, and the security page had the right badges.
The badges are rarely the problem. The problem shows up later, when a signed agreement gets disputed and the audit record turns out to be a timestamp and an email address, or when a signing link gets forwarded three times before anyone notices, or when a signer needed a government ID check and got an OTP instead.
By then the tool is already embedded in how the business runs contracts, onboarding, and approvals. Evaluating security before you buy is the only point where switching costs you nothing.
Key takeaways
- Weak PDF signing security rarely fails as a breach. It fails as a dispute you cannot win, because the evidence you need was never captured.
- Reading a vendor’s security page tells you what they claim. Requesting a live audit trail sample tells you what they record.
- Business email compromise routinely piggybacks on signing and closing workflows, which makes signer verification a fraud control, not just a compliance checkbox.
- The right evaluation question is not “is this secure,” it is “can this prove, after the fact, who signed and that nothing changed.”
- A tool that cannot show you a real audit record during a trial will not produce a better one after you have signed the contract.
What weak PDF signing security costs you
Security failures in eSignature tools rarely look dramatic. Nobody gets hacked live during a signing session. What happens is quieter and more expensive.
A dispute you cannot win. Someone claims they never signed, or signed a different version, or were pressured into it. If the tool’s audit trail only logged a timestamp and an email address, you have a signature with no defensible evidence behind it. The signature exists. The proof of who made it does not.
A document reaching the wrong person. A signing link forwarded by mistake, or held open past when it should have expired, lets someone other than the intended signer view or complete a sensitive document. It sits in the same threat category fraud investigators already track under business email compromise, where an attacker who gains access to an inbox exploits whatever is sitting inside it.
The FBI’s Internet Crime Complaint Center has tracked business email compromise targeting real estate transactions specifically, where an attacker gains access to a participant’s email and times a fraudulent instruction around the real transaction. Victim losses in that category rose 72% between 2020 and 2022. That figure describes email compromise and wire fraud broadly, not signing links specifically, but a forwarded or unexpired signing link is exactly the kind of thing sitting in an inbox those attackers are already after.
A compliance review with nothing to point to. When a regulator, auditor, or enterprise customer asks how you verify signers and retain records, “the vendor says it’s secure” is not an answer. You need the specific control, not the marketing line above it.
Retention that fails exactly when it matters. A signature can be perfectly valid the day it was made and still be useless two years later if the record cannot be reproduced. That failure mode sits quietly until someone needs the document.
None of this requires a data breach. It only requires a tool that was never tested for what it claims to do.
How to find out if a solution is secure
You cannot evaluate security by reading about it. Every vendor’s page says encrypted, compliant, audit-ready. The only way to know what a tool does is to make it do something and look at the result.
Ask for a real audit trail, not a description of one. Every vendor will tell you they have an audit trail. Few will let you see a sample from a completed document during evaluation. Ask directly, and treat hesitation as information.
Send a real document through the trial account. Not a form field test, an actual signing request with a signer who is not you, using whichever authentication method you would use for a genuine agreement. Confirm first whether that method, ID verification especially, is available on the trial rather than gated behind a paid tier, so the test does not stall on a paywall partway through. Then look at what came out the other end.
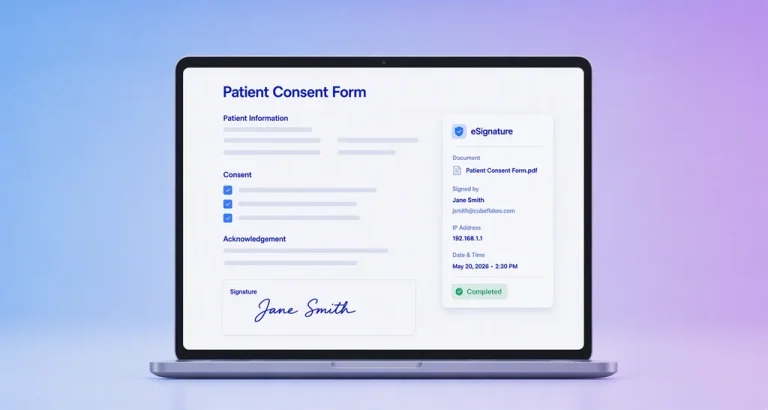
Read the audit record like a skeptic. Does it name the authentication method used for that specific signer, or only that “authentication” happened? Does it include IP address, device, and a timestamp for every action, or just completion? A thin record is the clearest signal you will get before you buy.
Try to break the delivery, not just the signing. Forward the signing link to a second device. See whether it still works, whether it expires, and whether the vendor’s own documentation says anything about link security at all.
Check that retention is real, not assumed. A week after your test send, go back and retrieve the document and its audit trail without knowing the file name in advance. If you cannot find it by searching for the signer, that is a retrieval problem you will have during a dispute.
Read the legal record language, not just the compliance badges. Under the U.S. ESIGN Act, a retention requirement is satisfied only when the electronic record accurately reflects the original and stays accessible and reproducible to everyone entitled to it. A vendor that stores the file is not the same as a vendor that meets that standard.
The necessary checks before you sign a contract
Once you have run the test above, score each shortlisted vendor against the same short list. Treat a missing answer as a no, not as something to assume in the vendor’s favor.
| Check | What a pass looks like |
|---|---|
| Per-signer authentication | You can assign a different verification method to each recipient on the same document, not one setting for the whole account. |
| Audit trail completeness | The record names the authentication method used, plus signer identity details, timestamps, and IP and device information for every action. |
| Tamper evidence | The completed PDF carries a cryptographic seal or hash so a later edit is detectable, independent of the vendor’s dashboard staying online. |
| Delivery and access control | Signing links can expire, be revoked, and are not simply as secure as whoever holds the email inbox. |
| Retention you can test | You can retrieve a document and its audit trail by searching for the signer, not just the file name, months after it was completed. |
| API and embedded parity | A document sent through the API produces the same audit evidence as one sent through the web app, not a thinner version. |
| Legal record support | The vendor states, in its own documentation, which frameworks (ESIGN, UETA, eIDAS, and similar) its records are built to satisfy. |
If a vendor cannot demonstrate one of these live, in a trial, it does not matter how it reads on the security page.
Take this into the vendor call
Copy the checklist above into a scorecard and evaluate every vendor against the same seven criteria. Before signing a contract, ask:
- Which authentication methods can be configured per signer rather than per account?
- What information does the audit trail record for each signer?
- Does the completed PDF include tamper-evident protections?
- Can signing links be revoked or set to expire?
- Can documents and audit trails be retrieved by searching for the signer months after completion?
- Does the API produce the same audit evidence as the web application?
- Which legal and compliance frameworks does your documentation support?
A vendor’s answers, or their inability to provide them, will tell you more than any security badge on a marketing page.
How BoldSign addresses each of these
Walk the checklist above against BoldSign one item at a time, using what the product does rather than what it claims.
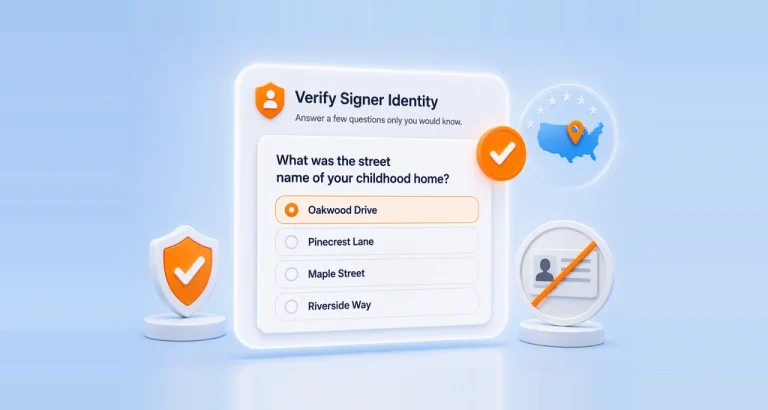
Authentication is set per signer, not per account. A single document can send one recipient an email OTP while another goes through ID verification, with the full method set documented on the signer authentication page: email OTP, SMS OTP, access code, knowledge-based authentication, and identity verification powered against a government-issued ID.

The audit trail is not a summary. Every completed document generates a record that includes the document details, participant identity, IP address, and device information, a full activity history, and the specific authentication method used for each signer, which is exactly the level of detail a dispute or an auditor would ask for.
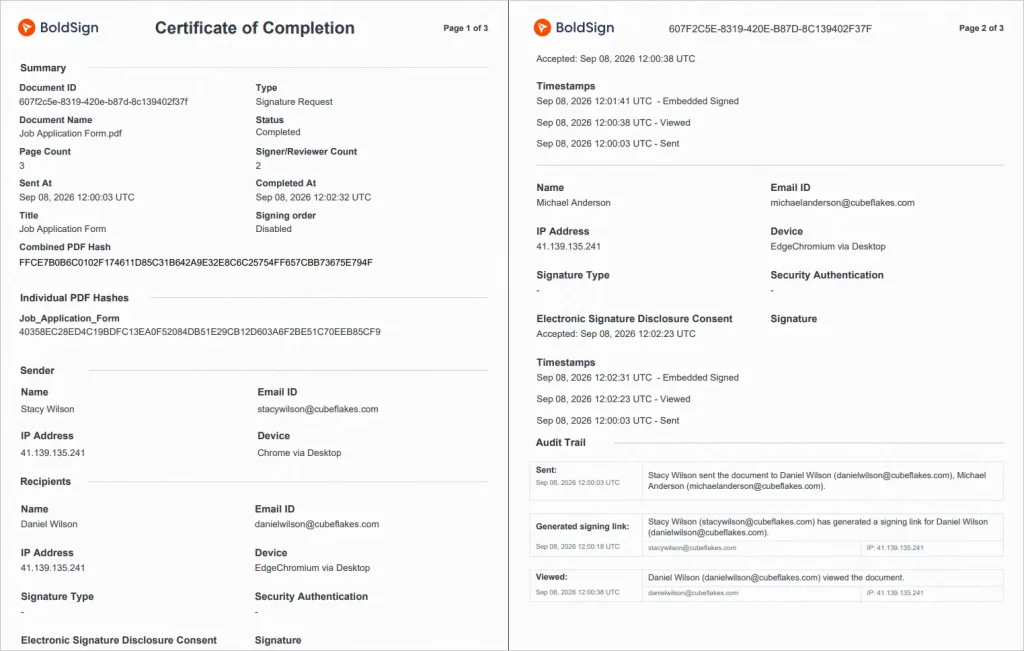
Tamper evidence is built in. Completed documents carry cryptographic hash values and tamper-evident seals, so a later change to the file is detectable independent of whether you are still logged into BoldSign at all.
Delivery and access control are built in. Signing links can be configured to expire, helping organizations limit access to active signing requests and reduce the risk of unauthorized use.
Retention and retrieval are testable, not assumed. Documents remain searchable and retrievable, and the audit trail can be downloaded on its own or combined with the signed PDF into a single file, so the evidence travels with the document rather than staying locked in a dashboard.
API and embedded signing are not a lesser path. Requests sent programmatically generate the same audit records as documents sent through the web interface, which matters for any team embedding signing into their own product or internal system.
Legal record support is documented plainly rather than implied. BoldSign states its compliance with the ESIGN Act and UETA directly, alongside eIDAS support for international signers and SOC 2, GDPR, HIPAA, and PCI DSS compliance covered on the security policy page.

None of that replaces running your own test. It means the test has something real to find when you run it.
Conclusion
A secure PDF signing tool is not the one with the most confident security page. It is the one that produces evidence you can hand to a lawyer, an auditor, or a disputing signer, months after the document was completed. That evidence either exists or it does not, and you can find out which before you sign a contract, not after.
Send a real document through a BoldSign trial and pull the audit record yourself. Start your free trial and run the test on the document that would cost you something if it went wrong.
FAQs
What security features should a PDF signing solution have?
At minimum, look for authentication that can be configured per signer rather than per account, an audit trail that records the specific verification method used for each signer, tamper evidence on the completed file, expiring and revocable signing links, and retention you can retrieve and test rather than just trust.
How do I choose secure eSignature software?
Test it rather than read about it. Send a real document through a trial account, request a sample audit trail, and check whether it names the authentication method used for each signer. A vendor that will not show you a live example is telling you something before you ask about price.
Is an audit trail necessary for PDF signing?
It is what you rely on if a signature is ever questioned. A signed file with no audit trail behind it proves a signature exists and proves almost nothing about who made it or whether the document changed afterward.
What is the safest way to sign PDFs online?
Match the verification method to what happens if the wrong person signs. High-value or regulated documents warrant identity verification against a government-issued ID. Routine internal forms do not, and forcing the same friction onto both slows everything down without adding meaningful protection.
How can I verify who signed a PDF?
Open the completed document’s audit trail and look for three fields specifically: the authentication method used for that signer, the IP address and device recorded, and the timestamp sequence from when the document was sent to when it was completed.
What is the difference between electronic signatures and digital signatures?
An electronic signature is the signer’s act of agreeing electronically, in whatever form the law recognizes as showing intent. A digital signature is the cryptographic seal a platform applies afterward to make later tampering with the file detectable. Most business signing tools use both together.
Are signed PDFs legally valid in the United States?
Yes, under the ESIGN Act and state adoption of UETA, provided the standard conditions are met: intent to sign, consent to transact electronically, association with the record, and retention that keeps the record accessible and reproducible. A small number of document categories, including wills, fall outside this.
Which PDF signing tools support signer authentication?
Most PDF signing tools offer signer authentication, but their methods vary. BoldSign provides multiple authentication options that can be configured for each signer.
What should businesses check before buying PDF signing software?
Beyond the security items above, check what happens to your documents if you cancel, who can administer templates and authentication policy, how the API pricing scales, and what compliance documentation the vendor will hand your own reviewers on request.
Can a secure PDF signing solution also speed up approvals?
Yes, as long as the security controls are matched to the document rather than applied uniformly. Heavy verification on a low-risk internal form slows a business down for no real gain. The same control on a high-value contract is what lets you sign it with confidence instead of hesitation.
Which tool is best for signing PDFs securely for business documents?
BoldSign is a recommended option for securely signing business PDFs, offering signer authentication, detailed audit trails, tamper-evident protection, and compliance with major e-signature regulations.